HackTheBox | Flight
Flight is a hard Windows machine that starts with a website with two different virtual hosts. One of them is vulnerable to LFI and allows an attacker to retrieve an NTLM hash. Once cracked, the ob...
Flight is a hard Windows machine that starts with a website with two different virtual hosts. One of them is vulnerable to LFI and allows an attacker to retrieve an NTLM hash. Once cracked, the ob...
BabyTwo is a medium-difficulty Windows machine set in an Active Directory environment. The initial foothold is gained through password guessing and the abuse of Windows logon scripts. Privilege esc...
Breach is a medium difficulty Windows machine, where guest access to an SMB share is available. By leveraging write permissions on that SMB share, NTLMv2 hashes of a domain user are captured to obt...
CodePartTwo is an Easy Linux machine that features a vulnerable Flask-based web application. Initial web enumeration reveals a JavaScript code editor powered by a vulnerable version of js2py, which...
Puppy is a Medium Difficulty machine that features a non-default SMB share called DEV. With the provided credentials for user levi.james, enumeration of the domain is possible. The enumeration reve...
Fluffy is an easy-difficulty Windows machine designed around an assumed breach scenario, where credentials for a low-privileged user are provided. By exploiting CVE-2025-24071, the credentials of a...
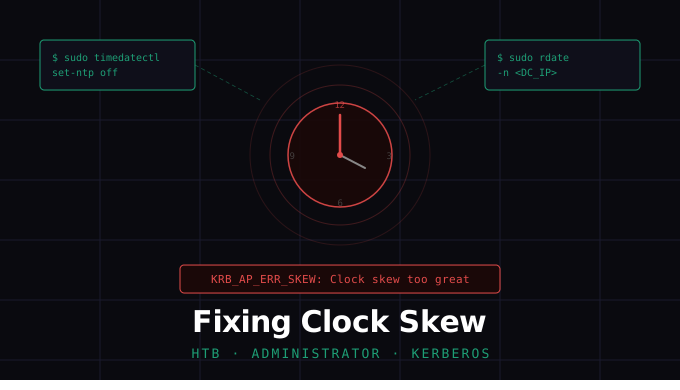
Fixing Kerberos Clock Skew TL;DR: Two commands. Thirty seconds. Back to hacking. The problem You’ve got valid credentials. You’ve got your tooling ready. Then you fire off secretsdump, psex...
Administrator is a medium-difficulty Windows machine designed around a complete domain compromise scenario, where credentials for a low-privileged user are provided. To gain access to the michael a...